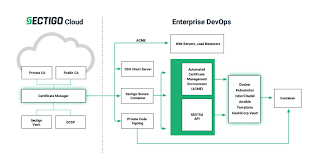
Originally reported by Help Net Security (September 2019). Source attribution: helpnetsecurity.com
Overview
Sectigo, a commercial Certificate Authority (CA) and PKI management vendor, announced integrations between its Sectigo Certificate Manager platform and five widely used DevOps configuration management and container orchestration tools: Docker, Kubernetes, Ansible, Terraform, and HashiCorp Vault. The stated goal is to give operations teams a single, centralized control plane for issuing, renewing, and revoking certificates across heterogeneous DevOps environments—without requiring deep PKI expertise from every team member who touches infrastructure.
Why PKI in DevOps Is Difficult
Modern DevOps environments are composed of hundreds or thousands of short-lived containers and microservices, each of which may need a certificate for mutual TLS authentication, service identity, or compliance purposes. This creates several practical challenges:
- Scale: Certificate volumes grow rapidly as container counts increase. Manual issuance and renewal does not scale.
- Short lifetimes: Containers and ephemeral workloads may live for minutes or hours, making traditional certificate lifecycle processes impractical.
- Decision complexity: IT generalists operating DevOps pipelines must make choices about key sizes, certificate term lengths, and trust hierarchies—topics that normally require specialized PKI knowledge.
- Compliance and auditability: Regulated industries require proof that certificates were issued according to policy and that expired or revoked certificates are tracked.
As Lindsay Kent, Sectigo’s VP of Product Management, noted at the time: organizations implementing DevOps often find themselves needing to become PKI experts overnight, selecting and configuring public key schemes without a background in the field. Mistakes in key management or certificate policy can leave containerized environments exposed or out of compliance.
How Sectigo Certificate Manager Integrates
Sectigo Certificate Manager connects to the supported DevOps tools using one of two mechanisms:
- ACME (Automated Certificate Management Environment): The IETF-standardized protocol (RFC 8555) used by tools such as cert-manager for Kubernetes, enabling fully automated certificate issuance and renewal without human intervention.
- Sectigo RESTful APIs: For tighter integration scenarios where custom workflows, certificate policy enforcement, or reporting are required.
Enterprises that already use a different CA or PKI implementation for issuance can still use Sectigo Certificate Manager in monitoring and reporting mode—tracking certificate deployments across their environment without migrating issuance workflows.
The Five Integrations Explained
Docker
Docker packages applications into portable containers that run consistently across environments. The Sectigo integration allows the platform to issue short-lived public or private TLS certificates directly to applications running inside Docker containers. This is particularly relevant when containers expose HTTPS endpoints or need client certificates for service-to-service authentication.
Kubernetes
Kubernetes automates deployment, scaling, and management of containerized workloads. The Sectigo integration works with the Kubernetes-native certificate controller, enabling certificate issuance and renewal to follow the same declarative, manifest-driven workflow that Kubernetes operators already use. Teams can define certificate resources as part of their cluster configuration and have Sectigo Certificate Manager fulfil those requests automatically.
Ansible
Ansible is a popular agentless configuration management and server provisioning tool. Sectigo’s Ansible module targets lifecycle management for large certificate volumes across heterogeneous environments—covering a mix of Linux, Windows, and other platforms from a single playbook. The module abstracts away complex security decision-making, providing a platform-agnostic interface for provisioning and managing both TLS server certificates and client certificates at scale.
Terraform
Terraform is an open-source infrastructure-as-code tool from HashiCorp that provisions and modifies infrastructure across cloud and on-premises environments. Sectigo’s Terraform provider enables enrollment, retrieval, and revocation of certificates as part of infrastructure provisioning workflows. When combined with HashiCorp Vault, Terraform can provision infrastructure while Vault handles secure storage of the resulting certificates and private keys.
HashiCorp Vault
HashiCorp Vault provides centralized secrets management, controlling access to passwords, API keys, and certificates based on application identity and user identity. Sectigo Certificate Manager can assign certificates to applications protected by Vault and store the private keys and certificates used across DevOps environments inside Vault’s encrypted secrets engine. This combination addresses both the issuance side (Sectigo) and the secure storage and access-control side (Vault) of certificate management.
Industry Context
Fernando Montenegro, Principal Analyst at 451 Research, commented on the announcement: “Certificate-based authentication is a foundational element in many DevOps use cases, and one that often grows in complexity when an enterprise considers details such as public versus private servers, client authentication, and more. We see a notable benefit for organizations to be able to use certificate management platforms that can address this complexity while integrating with popular configuration management and orchestration tools.”
The observation reflects a broader industry trend: as zero-trust network architectures gain traction, certificate-based mutual authentication between services is becoming a baseline requirement rather than an optional hardening step. Tools that bridge the gap between PKI operations and DevOps toolchains reduce the friction of adopting these practices at scale.
Key Takeaways for DevOps and Platform Engineering Teams
- Automated PKI integrations reduce the manual toil of certificate management in environments with high container churn.
- Using ACME or native API integrations means certificate issuance and renewal can be driven by the same infrastructure-as-code tooling already in place—no separate certificate management workflow required.
- Centralized reporting and monitoring across multiple issuance sources helps satisfy compliance and audit requirements without requiring teams to query individual tools.
- Separating issuance policy (managed by a CA platform) from deployment tooling (Ansible, Terraform, Kubernetes) gives security teams policy control without blocking DevOps velocity.
- HashiCorp Vault integration addresses the private key custody problem: even if a CA issues a certificate, the private key needs secure, audited storage with access controls—Vault provides that layer.
This article is based on a Sectigo press release and Help Net Security report from September 2019. Integration capabilities and product features may have changed since the original announcement. Consult Sectigo’s current documentation for up-to-date integration details.