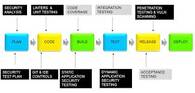
This article is based on research originally published on Security Boulevard covering enterprise DevSecOps practices.
Why DevSecOps Is Hard for Security Teams
DevOps is not purely a technology problem — it is largely a people and culture problem. Development and operations teams have largely internalized this. Security teams, however, still struggle to fit naturally into a model built around speed, continuous delivery, and automation.
This tension gives rise to the term DevSecOps: the intentional, structured integration of security practices into a DevOps pipeline. It is worth noting that your development and operations counterparts may push back on the label itself. To them, security is simply part of how code gets built and shipped — not a separate discipline bolted on. The distinction matters for security practitioners, though, because the integration is genuinely harder from the security side. Security teams must find ways to deliver secure code without creating bottlenecks in a delivery process they did not design and may not fully understand.
The good news: security fits well within a DevOps model when it is embedded into the automation and orchestration already in place. The sections below describe the concrete responsibilities security professionals need to own in order to make that happen.
Core Responsibilities of the Security Professional in a DevOps Environment
1. Learn the DevOps Model
You cannot influence a process you do not understand. Before pushing security requirements onto a development team, invest time learning how DevOps actually works — the cultural philosophy, the iterative delivery model, the toolchain, and how priorities are set. Understanding the mechanics of CI/CD pipelines, infrastructure-as-code, and sprint-based planning will give you the context you need to integrate security requirements in ways the team can actually act on.
2. Learn How to Be Agile
In a DevOps environment, security must conform to the process — not the other way around. DevOps optimizes for fast, iterative change with quick feedback loops and minimal Work In Progress (WIP). Security requirements that introduce large, slow gates will be worked around or ignored.
Instead, break security requirements into small, automatable steps. Manual processes like code reviews or fuzz testing are valid, but you need to be explicit about where they fit in the pipeline and which ones can block a release versus which ones are advisory. Shifting security culture from “feature first” to “secure by default” is a long-term effort — small, consistent improvements are more durable than big-bang mandates.
3. Educate the Development Team
Training remains one of the most effective ways to raise the security baseline of a development team. Options include in-house workshops, third-party application security consultants, threat modeling sessions, eLearning platforms, and commercial certification courses. Cost is a real constraint: a practical approach typically combines broad eLearning for all engineers with targeted in-person or instructor-led training for key individuals, who then share knowledge with their peers.
4. Build a Security Champion Network
Security teams are typically small — often outnumbered by developers at a ratio of 100:1 or more — and are rarely present in day-to-day agile ceremonies. You cannot scale security knowledge without embedding advocates inside development teams. Identify developers who are interested in security and formalize their role as security champions: people who surface security concerns during standups and sprint planning, review security-relevant pull requests, and serve as a first point of contact between the team and the security function. This model extends the security team’s reach without requiring proportional headcount growth.
5. Help the DevOps Team Understand Real Threats
Most developers do not have a deep intuition for how attackers think or what specific vulnerability classes actually enable in practice. Abstract warnings about “SQL injection” or “insecure deserialization” are easy to dismiss. Concrete, real-world examples are not.
Use resources like the OWASP Top Ten as a starting point, but go further: map vulnerability classes to real incidents, explain what the business impact of a credential exposure or data exfiltration event actually looks like, and walk through specific exploitation paths. Showing a developer what a SQL injection attack produces — not just that it is possible — is far more motivating than a policy document.
6. Advise on Remediation Practices
Generic guidance such as “encrypt sensitive data” or “deploy a WAF” is not a remediation plan. Developers and operations engineers need specific, actionable direction. Help build out the elements of your organization’s security program, covering both in-code controls and supporting infrastructure. Create accessible reference materials — a wiki page covering secure coding patterns, for example — written for readers without a security background. Security coding guidelines are more useful when they are discoverable, readable, and maintained alongside the codebase rather than buried in a PDF that nobody reads.
7. Help Evaluate and Select Security Tooling
Developers rarely evaluate security tools rigorously. Vendor marketing frequently overstates capabilities, and it is uncommon for engineering teams to assess whether a SAST scanner, activity monitor, or patch management system actually delivers meaningful results for their specific codebase and threat model.
Security professionals can add value in two ways here. First, guide tool selection: help the team understand what each tool actually does, where it fits in the testing pipeline, and what its limitations are. Second, help make the business case: security and compliance requirements are often opaque to budget holders. Define the functional and reporting requirements a tool must meet to satisfy both security objectives and regulatory obligations, and frame the investment in business terms.
8. Help Prioritize Vulnerabilities
A common failure mode for security teams is treating every finding as urgent. When everything is high severity, nothing gets fixed effectively. Exposure analysis — assessing which vulnerabilities pose real, exploitable risk to your specific environment — is a skill that sits squarely in the security domain and should not be delegated to developers.
Instead of issuing vague severity ratings, present tradeoffs. For a given vulnerability, options might include remediating it directly in code, patching a supporting system, disabling the affected feature, blocking exploitation at the network layer with IDS or firewall rules, or mitigating with WAF or RASP controls. In some cases, when exploitation cannot realistically harm the business, the correct answer may be to accept and document the risk rather than divert engineering effort. Giving the team options — with clear context about business impact — produces better outcomes than issuing a mandatory fix-everything directive.
9. Write Tests and Contribute to Automation
Security requirements that live only in documentation rarely make it into production. Security requirements encoded as automated tests always do. Contribute concrete tests to the CI/CD pipeline: certificate validation checks, known injection attack patterns, open-source vulnerability scanning steps, and regression tests for previously identified issues.
You do not need to be an expert software engineer to start. Developers are generally willing to help translate security logic into the correct scripting format or pipeline syntax. Learning the basics of the team’s scripting language or infrastructure-as-code tooling will make you a more effective contributor and signal to the team that security is a shared responsibility rather than an external audit function. Policies embedded in pipeline code are enforced automatically; policies in slide decks are not.
10. Act as a Policy and Compliance Advisor
Corporate security policy, privacy regulations, and software licensing requirements are frequently opaque to development teams. A CVE identifier tells a developer almost nothing about how to remediate a vulnerability in a way that satisfies compliance requirements. Internal security policy documents are often inaccessible or poorly written for a developer audience.
Position yourself as the team’s advisor on these topics. You should have a deeper working knowledge of compliance frameworks, data privacy obligations, and acceptable-use policies than anyone on the development team. Making yourself available as a resource — rather than appearing only to audit or block — builds the trust that makes DevSecOps collaboration sustainable over time.
Summary
Integrating security into a DevOps pipeline requires more than deploying scanning tools. It requires security professionals to understand how DevOps teams work, communicate in terms those teams can act on, and contribute directly to the automation and testing infrastructure that drives delivery. The responsibilities outlined above are not aspirational — they are the practical baseline for a security function that wants to be a trusted partner rather than a speed bump in the software delivery process.