This article is based on a webinar Q&A session hosted by Docker in early 2017, in which Harish Jayakumar, Solutions Engineer at Docker, answered audience questions about Docker Datacenter (DDC) for AWS. The original source is docker.com. Pricing and feature details reflect the state of the product at the time of publication.
Background
Docker Datacenter (DDC) is Docker’s enterprise container management platform, combining Universal Control Plane (UCP) for cluster orchestration and Docker Trusted Registry (DTR) for private image management. At AWS re:Invent 2016, Docker announced a CloudFormation-based deployment template that makes it significantly easier to stand up a full DDC stack on an AWS EC2 cluster. The questions below were submitted live by the webinar audience and represent the most common concerns raised by AWS users evaluating DDC as an enterprise container platform.
Infrastructure and Networking
Q1: How many VPCs are required to create a full cluster of UCP, DTR, and worker nodes?
A: The DDC CloudFormation template creates one new VPC, along with the necessary subnets and security groups. If you want to use DDC within an existing VPC, you can deploy DDC manually without using the CloudFormation template.
Q7: Is there a single endpoint in front of the three UCP manager nodes?
A: Docker recommends deploying three UCP manager nodes to ensure high availability. You can place an AWS Elastic Load Balancer (ELB) in front of those three managers so that clients connect to a single endpoint rather than addressing each manager by its individual IP.
Q9: Can I configure my Docker CLI to point to that single load-balanced endpoint?
A: Yes. Once an ELB (or equivalent) is configured in front of the manager nodes, you can target it from your Docker CLI client bundle.
Q10: What are the infrastructure requirements to run DDC on-premises with three UCP managers and three workers?
A: The CloudFormation template handles resource sizing automatically for AWS deployments. For on-premises or custom deployments outside of CloudFormation, consult the official Docker documentation for DDC infrastructure requirements, which covers CPU, RAM, and disk minimums for both manager and worker nodes.
Q15: Is DDC for AWS dependent on AWS EBS?
A: EBS volumes are used for the EC2 instances themselves, functioning as local disk cache rather than persistent storage. Any data stored on an EBS volume tied to an instance will be lost if that instance is terminated. For stateful workloads requiring durable storage, a separate persistent storage strategy should be planned.
Pricing and Licensing
Q2: Is the $150/month cost per EC2 instance?
A: Yes, the pricing at time of publication was $150 per EC2 instance per month under the monthly subscription model, available directly through Docker Store. Annual subscriptions were also available at $1,500 per node per year or $3,000 per node per year depending on tier. Note: These prices are from early 2017 and are almost certainly out of date. Check the current Docker pricing page for up-to-date figures.
Container Management and Observability
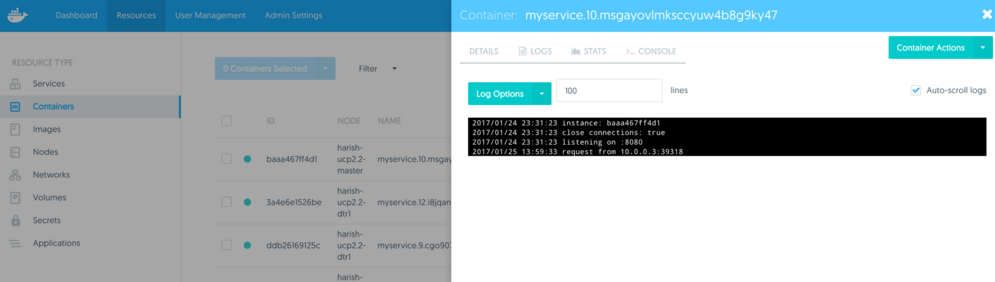
Q3: How do you view logs for individual containers in the UCP UI?
A: In the UCP web interface, navigate to Resources → Containers. Select any individual container from the list to view its log output directly within the UI.
Q4: How does resource allocation work? Can you over-allocate CPU or RAM?
A: Docker provides flexible resource controls at the container level:
- CPU: By default, a container’s access to host CPU cycles is unlimited. You can set constraints to limit CPU usage per container.
- Memory (hard limit): Docker can enforce a strict upper bound on memory, preventing a container from using more than the specified amount of user or system memory.
- Memory (soft limit): A softer constraint allows a container to use as much memory as needed unless the kernel detects low memory or resource contention on the host, at which point it may reclaim memory from that container.
Q6: Can DDC trigger alerts based on user-defined criteria such as resource utilization?
A: Docker is event-driven, and it is possible to configure alerting based on those events. Within the UCP UI, resource utilization is visible, and notifications can be associated with specific events. For more sophisticated alerting pipelines (e.g., integrating with PagerDuty or Slack), additional tooling and configuration are typically required.
Security and Access Control
Q5: Can console access via UCP be restricted using RBAC?
A: Yes. UCP includes role-based access control (RBAC) that can be used to restrict console access and other operations. Docker published a dedicated blog post explaining UCP access controls in detail at the time of the webinar (originally linked as http://dockr.ly/2jNjK86).
Q8: Do you have to use DTR, or can you use alternative registries like AWS ECR or Artifactory?
A: When deploying via the CloudFormation template, DTR is the integrated registry. DTR and UCP share components and have single sign-on (SSO) enabled via the same LDAP/AD directory. Critically, the secure software supply chain — including image signing and vulnerability scanning — only functions end-to-end when using the full DDC stack. UCP can be configured to refuse to run containers from images that have not been signed by DTR, a capability Docker calls policy enforcement. Using an alternative registry is technically possible for manual deployments, but you lose these integrated security guarantees.
Routing and Service Discovery
Q12: If you don’t use the routing mesh, how do you route to individual containers? Is single-tenant architecture (one container per user) possible?
A: The routing mesh is built into the Docker engine (available since Docker 1.12) and is enabled by default. It routes traffic to containers cluster-wide without requiring clients to know individual container IPs. Before Docker 1.12, you had to route explicitly to a specific container and port. UCP also supports routing by hostname mapped to specific services, and Docker’s built-in DNS can resolve container names as aliases. Single-tenant architectures (one container per user) are architecturally possible, though the routing and resource isolation design must be planned carefully.
State Management and Orchestration Internals
Q13: Does DDC use Consul as a key/value store for the overlay network?
A: No. Docker Swarm mode does not require an external key/value store such as Consul or etcd. Cluster state is stored in a distributed database on the manager nodes using the Raft consensus algorithm (often referred to as the Raft store). Manager nodes form a Raft consensus group, elect a leader, and that leader maintains authoritative state including the list of nodes, services, and tasks across the swarm, as well as scheduling decisions.
Q14: How does node draining work in the context of AWS Auto Scaling Groups (ASGs)?
A: Draining a node in UCP does the following:
- Prevents the node from receiving new tasks from the manager.
- Stops tasks currently running on that node.
- Launches replacement replica tasks on nodes with ACTIVE availability.
The drained node remains part of the ASG group. Coordinating graceful draining with ASG scale-in events requires additional lifecycle hook configuration so that the node is drained before AWS terminates the instance.
CloudFormation Template and AWS Quick Start
Q11: How does the DDC for AWS demo compare to the AWS Quick Start for Docker DDC?
A: At the time of the webinar (early 2017), the demo and the AWS Quick Start for Docker DDC were functionally the same. Docker indicated that an updated version was forthcoming. Check the AWS Quick Start catalog and Docker’s official documentation for the most current deployment templates.
Summary
Docker Datacenter for AWS (now superseded by more recent Docker Enterprise and Mirantis offerings) provided a CloudFormation-based path to deploying UCP and DTR on EC2 with integrated RBAC, image signing, policy enforcement, and Swarm-based orchestration. The questions above cover the most common operational concerns: networking topology, pricing, logging, resource limits, security controls, registry choice, routing, internal state management, and AWS-specific integration points like ASGs and EBS. If you are evaluating a modern equivalent, review the current Docker Enterprise or alternative Kubernetes-based managed services on AWS (such as EKS) documentation for up-to-date architecture guidance.