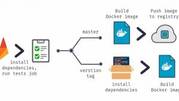
Container registries are a foundational piece of any container-based delivery pipeline. They store, version, and distribute container images — making them as critical to a containerized workflow as a package manager is to traditional software development. As container adoption has grown, so has the market for registry software, with both cloud-hosted and self-hosted options now available from a wide range of vendors.
What Is a Container Registry?
A container registry is a repository — or collection of repositories — that stores container images. Developers push images to a registry after building them and pull images from the registry when deploying to staging or production environments. Registries can be public (anyone can pull images) or private (access is restricted to authenticated users or services).
Key capabilities typically expected from enterprise-grade container registries include:
- Image versioning and tagging
- Role-based access control (RBAC)
- Vulnerability scanning of stored images
- Integration with CI/CD pipelines
- Replication across geographic regions
- Webhook support for automation
- Audit logging and compliance reporting
Major Vendors in the Container Registry Space
The container registry market includes both dedicated registry products and registries bundled within broader cloud or DevOps platforms. The following vendors are among the most widely referenced in enterprise and open-source contexts:
Microsoft Azure Container Registry (ACR)
ACR is tightly integrated with Azure Kubernetes Service (AKS) and Azure DevOps. It supports geo-replication, image signing, and automated builds triggered by source code commits or base image updates. ACR Tasks allow teams to offload container build and patching workflows to Azure.
Docker Hub and Docker Trusted Registry
Docker Hub is the most widely used public registry, hosting millions of official and community images. Docker also offered Docker Trusted Registry (DTR) as an on-premises enterprise option, though this has evolved through Docker’s various corporate transitions. Teams already using Docker Desktop and Docker Compose will find Hub the path of least resistance for public image distribution.
JFrog Artifactory
Artifactory is a universal artifact repository manager that supports Docker images alongside other package formats such as Maven, npm, PyPI, and Helm charts. This makes it attractive for organizations that want a single platform to manage all build artifacts rather than separate tools per ecosystem. JFrog also offers JFrog Xray for deep security scanning integrated with Artifactory.
Google Artifact Registry (formerly Container Registry)
Google’s registry offering integrates with Google Kubernetes Engine (GKE), Cloud Build, and Cloud Deploy. Google Artifact Registry superseded the older Google Container Registry and adds support for additional artifact formats beyond Docker images. Binary Authorization allows teams to enforce image signing policies before deployment to GKE.
Oracle Container Registry
Oracle provides a container registry as part of Oracle Cloud Infrastructure (OCI), aimed at organizations running Oracle workloads or deploying to OCI Kubernetes clusters. It distributes official Oracle software images and supports private repositories for customer workloads.
Red Hat Quay
Quay (originally from CoreOS, later acquired by Red Hat) is available as a hosted service at quay.io and as a self-hosted enterprise product. It is notable for built-in security scanning via Clair, time-machine rollbacks, and fine-grained repository permissions. It is a common choice in OpenShift environments.
IBM Cloud Container Registry
IBM’s registry service integrates with IBM Kubernetes Service and Red Hat OpenShift on IBM Cloud. It includes Vulnerability Advisor for image scanning and namespace-based access control.
Alibaba Container Registry (ACR)
Alibaba Cloud’s registry is the primary option for organizations running containerized workloads in mainland China and broader Asia-Pacific regions, where access to other registries may be restricted or slower. It integrates with Alibaba’s container service and DevOps toolchain.
VMware Harbor
Harbor is a CNCF-graduated open-source registry originally developed by VMware. It adds enterprise features on top of the OCI Distribution Specification, including image replication, LDAP/AD integration, vulnerability scanning, and content trust. As an open-source project, it can be self-hosted on any infrastructure.
Deployment Models: Cloud-Hosted vs. Self-Hosted
Container registries generally fall into two deployment categories:
Cloud-Hosted (SaaS) Registries
Services such as Docker Hub, Amazon ECR, Google Artifact Registry, Azure Container Registry, and GitHub Container Registry are fully managed. The provider handles infrastructure, availability, and scaling. These are the fastest option to get started and typically require no operational overhead for teams without dedicated platform engineering resources.
Self-Hosted Registries
Products such as JFrog Artifactory, Red Hat Quay, and Harbor can be deployed on-premises or in a private cloud. Self-hosted registries give organizations direct control over data residency, network latency for image pulls within a data center, and integration with internal identity providers. The trade-off is operational responsibility for uptime, storage, and upgrades.
Key Factors When Evaluating a Container Registry
Choosing a registry is rarely just a technical decision. The following factors are typically weighed during an evaluation:
- Security scanning: Does the registry scan images for known CVEs at push time, on a schedule, or both? How are results surfaced to developers?
- Access control: Does the registry support fine-grained RBAC, service account tokens, and integration with your identity provider (LDAP, SAML, OIDC)?
- CI/CD integration: How easily does the registry plug into your existing pipeline tools (Jenkins, GitHub Actions, GitLab CI, Tekton, etc.)?
- Replication and high availability: Can images be replicated to multiple regions to reduce pull latency and improve resilience?
- Image signing and provenance: Does the registry support Notary, Sigstore/cosign, or similar tools for supply chain security?
- Storage costs: For cloud-hosted options, understand egress and storage pricing — large image layers pulled frequently can generate significant cost.
- Multi-format support: If your teams also manage Helm charts, OPA bundles, or other OCI-compatible artifacts, a registry that handles multiple formats reduces tool sprawl.
- Compliance and audit: Regulated industries may require detailed audit logs, data residency controls, or certifications such as SOC 2 or ISO 27001.
Market Segments by Organization Size
Registry requirements differ significantly between large enterprises and smaller organizations:
Large Enterprises
Large organizations typically prioritize governance, compliance, and integration with existing identity and security tooling. Self-hosted options or premium tiers of cloud registries are common, and multi-registry federation (maintaining registries in multiple clouds or regions) is increasingly relevant for organizations pursuing a multi-cloud strategy.
Small and Medium-Sized Businesses (SMBs)
Smaller teams generally favor simplicity and low operational overhead. Managed cloud registries — particularly those bundled with a cloud provider already in use — are the most common choice. Free tiers from Docker Hub, GitHub Container Registry, or a cloud provider’s included registry quota often meet initial requirements.
Container Supply Chain Security: An Emerging Priority
Since approximately 2021, supply chain security has become a primary concern for teams operating container infrastructure. High-profile incidents involving compromised base images and malicious public registry packages have driven investment in:
- Image signing with tools like cosign (part of the Sigstore project)
- Software Bill of Materials (SBOM) generation and storage
- Policy enforcement at deploy time using tools like Kyverno or OPA/Gatekeeper
- Private mirrors of public registries to reduce exposure to upstream tampering
Modern registry selection should factor in how well the product supports these workflows, not just basic image storage and retrieval.
Summary
The container registry market has matured considerably, with strong options available for every scale and deployment model. Cloud-native teams often start with a managed registry from their primary cloud provider for simplicity, while organizations with stricter compliance, latency, or multi-cloud requirements frequently move toward self-hosted or hybrid approaches using products like JFrog Artifactory, Red Hat Quay, or Harbor.
When evaluating options, prioritize security scanning, access control, CI/CD compatibility, and supply chain features — not just storage cost and uptime SLAs. The registry sits at the center of your image delivery pipeline, and weaknesses there propagate directly into production.