Originally reported by Redmond Magazine. Post date: June 13, 2020.
AD DS Authentication for Azure Files Reaches General Availability
Microsoft announced that Active Directory Domain Services (AD DS) authentication for Azure Files has reached general availability (GA), meaning the feature is production-ready and supported under standard SLAs. The milestone is significant for enterprises that rely on on-premises Windows file share infrastructure and are looking to migrate workloads to the cloud without abandoning existing access control models.
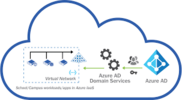
AD DS enables synchronization of on-premises Active Directory accounts with Azure Active Directory (Azure AD). When used with Azure Files, it allows existing on-premises Windows Access Control Lists (ACLs) to be applied directly to cloud-hosted file shares — meaning permissions defined on-premises carry over to Azure Files without requiring a manual rebuild of the permission structure.
How AD DS Integration Simplifies Cloud Migrations
The core value proposition for AD DS integration is migration simplicity. According to Microsoft, as long as on-premises servers or user laptops are domain-joined to AD DS, the workflow is straightforward:
- Sync your on-premises Active Directory to Azure AD.
- Enable AD DS authentication on the Azure storage account.
- Mount the Azure file share directly from domain-joined machines.
With this in place, Azure Files behaves like a traditional on-premises file share from the end user’s perspective. Existing Windows ACLs are seamlessly carried over and continue to be enforced for authorization, removing one of the most friction-heavy steps in a file share cloud migration.
Azure Files and Virtual Desktop Infrastructure (VDI)
Microsoft has been actively positioning Azure Files as a storage backend for Virtual Desktop Infrastructure (VDI) scenarios. The AD DS integration is particularly useful here because it enables single sign-on (SSO) for end users accessing file shares through virtual desktops, reducing friction and support overhead.
Azure Files in VDI deployments also benefits from cloud-native scalability — storage capacity can scale to meet demand without provisioning additional on-premises hardware. Microsoft has partnered with VDI vendors to support this use case. Notably, Citrix announced day-one support for Azure Files as a certified storage solution for both its User Profile Management and User Personalization Layer technologies at the time of this announcement.
Other Azure Files Enhancements Announced
Soft Delete (Preview)
Microsoft previewed a soft delete feature for Azure Files, which works similarly to a recycle bin. When a file share is deleted, the data is not immediately purged — administrators can configure a retention window during which soft-deleted snapshot data can be recovered. To restore content, it must first be explicitly “undeleted.”
At the time of announcement, the soft delete feature was turned off by default for both new and existing Azure Files accounts. Microsoft indicated it would be enabled by default for new accounts later in 2020, and enabled by default in the API beginning January 1, 2021.
Azure Backup Integration (GA)
Azure Backup support for Azure Files had already reached general availability in April 2020, prior to this announcement. Azure Backup stores read-only, point-in-time snapshots of file shares and supports policy-based retention at weekly, monthly, and yearly intervals — with a maximum retention period of up to 10 years.
Azure Backup also automatically prunes expired snapshots to keep deployments within the 200-snapshot-per-file-share limit enforced by the platform, reducing the operational overhead of snapshot lifecycle management.
Expanded Geo-Redundancy Options
Microsoft noted ongoing work to expand redundancy tiers for Azure Files. At the time of announcement:
- Geo-redundant storage (GRS) and geo-zone-redundant storage (GZRS) were available for standard file shares under 5 TB.
- Microsoft was actively working to extend GRS support to standard file shares of up to 100 TiB.
These expansions are aimed at organizations with large file share workloads that require regional failover capabilities for business continuity.
Key Takeaways for DevOps and Infrastructure Teams
- AD DS GA means you can now confidently use on-premises AD accounts and Windows ACLs with Azure Files in production without workarounds.
- VDI + Azure Files with AD DS provides SSO and scalable profile storage — evaluate Citrix and other supported VDI platforms for certified integrations.
- Soft delete adds a safety net against accidental file share deletion — plan to enable it proactively once it reaches GA.
- Azure Backup policies allow long-term snapshot retention (up to 10 years) with automatic pruning, reducing manual snapshot management.
- Geo-redundancy expansion to 100 TiB will be important for large-scale migrations — monitor Azure updates for availability timelines.
Note: This article reflects Microsoft announcements from June 2020. Feature availability, default settings, and size limits may have changed. Refer to the official Azure Files documentation for current specifications.