Kubernetes is an open-source platform for container management and orchestration. Containers are self-contained software packages that let developers bundle part or all of an application — along with its dependencies — into a single deployable unit. Containers simplify continuous integration and continuous delivery (CI/CD) pipelines and make it straightforward to move applications between environments. Kubernetes gives engineers and administrators the tools to monitor, manage, and orchestrate these discrete packages within a larger production environment. Failure response, configuration management, and application updates can all be automated through Kubernetes.
Origin and History
Kubernetes is directly descended from Google’s internal container cluster manager, Borg. Because its design lineage traces back to a system built for Google-scale workloads, Kubernetes is architecturally capable of managing very large, complex deployments.
Google open-sourced Kubernetes in 2014. The project attracted contributions from major technology companies and open-source organisations almost immediately. In 2016, Google donated Kubernetes to the Cloud Native Computing Foundation (CNCF), a vendor-neutral open-source organisation. Two years later, Kubernetes became the first project to graduate from the CNCF incubator program — a milestone that signalled its production readiness and broad community support. Today it remains one of the most actively contributed-to projects on GitHub.
Why Kubernetes Was Built: Distributed Systems at Scale
Kubernetes was designed from the ground up for cloud-native and distributed applications. Traditional deployment tools were not built to manage hundreds or thousands of container instances spread across multiple servers. Kubernetes solves this by providing a unified control plane that tracks and manages container workloads regardless of which physical or virtual machine they run on.
This makes Kubernetes especially well-suited for microservices architectures, where an application is broken into many small, independently deployable services that must discover one another, communicate reliably, and scale independently.
Cloud-Native and DevOps Use Cases
Kubernetes accelerates DevOps workflows by automating the most error-prone parts of application delivery and operations.
Rolling Updates Without Downtime
When developers push an updated version of an application, Kubernetes creates and deploys new containers incrementally in a rolling fashion. Horizontal scaling compensates for pods taken temporarily offline during the update, so end users experience no interruption in availability.
A pod is the smallest deployable object in Kubernetes — it is a collection of one or more tightly coupled containers that share network and storage resources.
Autoscaling
Developers can declare minimum and maximum pod counts in code. Kubernetes monitors resource consumption and autoscales the number of running pods to match demand. When traffic spikes, new pods are launched automatically; when traffic drops, idle pods are removed to reduce cost.
Automatic Rollbacks
Developers define a desired state for their containers. Kubernetes continuously checks that running containers match that state. If a newly deployed container is unhealthy or fails its health checks, Kubernetes automatically pulls it from production and reinstates the last known-good version — reducing mean time to recovery (MTTR) for bad deployments.
Core Kubernetes Features
Control Plane (Master Components)
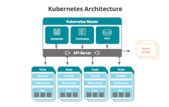
The Kubernetes control plane is responsible for all global decisions about the cluster. Its components handle scheduling (deciding which node runs which pod), detect cluster events (such as a pod crashing), and respond to those events automatically. Key control plane components include the API server, etcd (the cluster’s key-value store), the scheduler, and the controller manager.
Service Discovery and Load Balancing
Kubernetes assigns each pod an IP address and gives sets of pods a stable DNS name. Applications can use these DNS names to discover other services without hardcoding IP addresses. Kubernetes also load-balances traffic across healthy pods automatically, routing requests away from pods that are failing or under heavy load.
Storage Orchestration
Container filesystems are ephemeral — data written inside a container is lost when the container stops. Kubernetes solves this with volumes, which can be mounted into containers to provide persistent storage. Kubernetes supports a wide range of storage backends, including local disk, NFS, and cloud-provider storage services, through a pluggable volume interface.
Automated Deployment and Rollbacks
By declaring a desired state in a manifest file (typically YAML), developers instruct Kubernetes on how an application should run. Kubernetes then takes responsibility for converging the actual cluster state toward that desired state — deploying new containers when the desired state changes and rolling back to working versions when problems are detected.
Automatic Resource Bin-Packing
Operators can specify CPU and memory requests and limits for each container. The Kubernetes scheduler uses these declarations to place containers on nodes that have sufficient available resources, making efficient use of the underlying infrastructure without over-provisioning.
Secret and Configuration Management
Kubernetes provides two mechanisms for injecting configuration into containers without baking it into the container image:
- ConfigMaps — store non-sensitive configuration data such as environment variables or configuration files.
- Secrets — store sensitive data such as passwords, API tokens, and TLS certificates. Secrets are base64-encoded and access-controlled, giving operators fine-grained control over which pods can read which credentials. Kubernetes also automatically creates secrets containing credentials for its own API, used by pods that need to communicate with the control plane.
Summary
Kubernetes has become the de facto standard for container orchestration because it addresses the hardest operational problems in running distributed systems at scale: scheduling, self-healing, scaling, service discovery, storage, and secrets management — all through a declarative, API-driven model. Whether you are running a handful of microservices or thousands of containers across a global fleet of nodes, understanding these fundamentals is the foundation for effective cloud-native operations.
Original article based on content sourced from SDxCentral and the Kubernetes project documentation.