This article draws on concepts originally discussed at securityintelligence.com.
The Roots of Test-Driven Development
In 1999, Kent Beck’s Extreme Programming Explained: Embrace Change challenged conventional assumptions about how software should be built. Three years later, his follow-up book, Test-Driven Development: By Example (2002), gave the practice its canonical form and vocabulary. TDD has since become one of the most widely discussed methodologies in software engineering, with a large body of books, courses, and community resources devoted to it.
The Agile Alliance has documented the evolution of TDD alongside the broader Agile movement, noting how its core principles — write the test first, make it pass, then refactor — shaped the way teams think about software quality.
What TDD Actually Means: Test-First Plus Refactoring
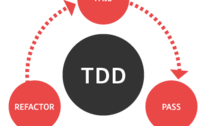
TDD rests on a deceptively simple premise: write the test before you write the code. This is sometimes called test-first development. The workflow follows a short, repeatable cycle:
- Red — Write a failing test that describes the desired behaviour.
- Green — Write the minimum code needed to make that test pass.
- Refactor — Improve the code without changing its observable behaviour, re-running all tests after every change.
The refactoring step is what separates TDD from simple test-first development. It mirrors continuous improvement frameworks such as the Deming (Plan-Do-Check-Act) cycle — each iteration leaves the codebase slightly cleaner and better understood than before.
For developers, TDD is a mindset change. Instead of writing code and hoping it works, you design a battery of assertions that must all pass before a feature is considered done. After every subsequent change, the entire test suite reruns, giving the team strong, repeatable assurances about the state of the system.
Three TDD Lessons for DevOps and Security Teams
TDD’s principles are not limited to application code. DevOps engineers and security practitioners can draw three concrete lessons from TDD and apply them to infrastructure, operations, and cyber resilience.
Lesson 1: Verify That Systems Are Working the Way They Should
Without automated tests, how can an organisation genuinely confirm that its systems are operating normally? The TDD principle of continuous, automated verification applies directly to infrastructure and security tooling:
- Network and system level: Automated checks can verify that firewalls are correctly configured, that routing rules are enforced, and that certificates are valid and unexpired.
- Security operations: Tests can confirm that an intrusion detection system (IDS) or SIEM is actively generating alerts in response to known-bad traffic patterns — not merely running as a process.
- Human and process level: Tabletop exercises and simulated incidents test whether personnel respond according to documented runbooks, surfacing gaps before a real event does.
Tools such as Chef InSpec, Testinfra, and cloud-provider compliance frameworks allow teams to encode these checks as executable specifications — the infrastructure equivalent of a TDD test suite.
Lesson 2: Don’t Deploy a New System Until You Know How to Test It
TDD insists that the test must exist before the code ships. The equivalent principle for infrastructure is: define your acceptance criteria and test harness before a system goes into production.
This is one of the hardest lessons to implement in practice, for two reasons:
- Complexity: Modern distributed systems — microservices, service meshes, multi-cloud architectures — are often too complex for any single person to fully understand, let alone test exhaustively.
- Resources: Meaningful pre-production testing requires an environment that faithfully mirrors production: representative data volumes, realistic network topology, and the same security controls.
Despite the difficulty, the cost of skipping this step is well documented. Organisations have repeatedly deployed patches or new systems without adequate testing, only to discover that the change degraded availability, introduced regressions, or weakened security controls — sometimes all three simultaneously. The CIA triad (Confidentiality, Integrity, Availability) provides a useful checklist for structuring pre-deployment tests.
Practices such as blue/green deployments, canary releases, and chaos engineering are direct implementations of this lesson at the operational level.
Lesson 3: Refactor Your Systems — and Eventually Your Entire Environment
The refactoring step in TDD is not optional cleanup; it is a first-class activity that keeps the codebase maintainable over time. The same discipline applied to infrastructure — enabled by Infrastructure as Code (IaC) — allows organisations to continuously improve their environments without accumulating technical debt.
Cloud-native and software-defined technologies make this practical in a way that hardwired, legacy environments do not:
- Software-defined networking (SDN) lets teams redefine network segmentation without physical recabling.
- IaaS and PaaS platforms allow entire environments to be torn down and rebuilt from version-controlled templates.
- Policy-as-code tools (e.g., Open Policy Agent, HashiCorp Sentinel) encode security guardrails that travel with the infrastructure through every refactor.
When Lessons 1 and 2 are in place — automated verification and pre-deployment testing — teams can refactor with confidence. The test suite catches regressions, and the organisation builds genuine cyber resilience rather than simply hoping the environment is secure.
A Shared Need for Change
TDD emerged from a collective recognition in the software industry that the old way of building and testing code was not good enough. Cybersecurity and DevOps have reached an analogous inflection point: perimeter-based, reactive security is insufficient against determined attackers and increasingly complex infrastructure.
Applying TDD’s three core lessons — continuous verification, test before deploy, and systematic refactoring — gives teams a practical framework for improving the resilience of systems incrementally and measurably, rather than through one-off audits or hope-driven deployments.
Key Takeaways
- Test first: Define what correct behaviour looks like before you build or deploy anything.
- Automate verification: Manual checks do not scale; encode your assertions as executable tests.
- Refactor continuously: Use IaC and software-defined infrastructure to improve environments safely, backed by a reliable test suite.
- Apply to people and processes, not just systems: Tabletop exercises and simulated incidents are the human equivalent of a TDD test run.