If you have ever hired security professionals, you already know the talent shortage is real. Compensation for security specialists has been growing faster than for most other IT roles, and competition for qualified candidates remains fierce. The hiring process can stretch for months, leaving critical gaps in your security posture in the meantime.
The answer is not simply to hire more people — it is to make the people you have dramatically more effective. Organizations that embed security thinking across their engineering and operations teams multiply the impact of every security hire. Below are five concrete tips that help you do exactly that.
1. Get Your DevOps Team On Board With SecOps
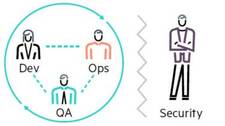
If your development and operations teams are already working in a DevOps model, the next logical step is to extend that collaboration to security — commonly called DevSecOps or SecOps. Train the people who write and deploy code to treat security as part of their everyday responsibility, not as someone else’s problem to clean up later.
This cultural shift must be driven from leadership. When security metrics appear on the same dashboards as deployment frequency and uptime, engineers begin to internalize security as a first-class concern. Reinforce that expectation in code-review checklists, sprint retrospectives, and performance evaluations.
2. Bring Security Alerts Into DevOps Workflows
Asking developers to log into a dedicated security console they rarely visit almost guarantees that alerts will be ignored or actioned too slowly. Instead, deliver security signals where engineers already spend their time.
ChatOps platforms such as Slack, Microsoft Teams, or Mattermost are an effective bridge. Routing security alerts into a dedicated channel — or even into team-specific channels — means engineers see relevant alerts in context, can discuss them immediately, and can escalate or dismiss without context-switching to an unfamiliar tool.
The lower the friction, the more consistently your team will respond to alerts in a timely and repeatable way. Enrich alerts with contextual metadata — the host, the process, the user account involved — so the people reviewing them can triage quickly without needing deep security expertise.
3. Extend Security Visibility Across the Whole Organization
Do not stop at the engineering team. When security awareness tools and channels are accessible to everyone — product managers, support staff, finance — you gain a much larger set of eyes watching for anomalies.
Practical ideas include:
- A company-wide
#securitySlack channel where anyone can flag suspicious emails, unusual login prompts, or strange behavior. - Automated alerts that ping the individual user whose action triggered a security event, asking them to confirm or deny — this dramatically speeds up triage.
- Regular, short security digests that keep the broader team informed about active threat patterns without overwhelming them.
Building this culture of openness and shared responsibility makes your organization a harder target and reduces the burden on your dedicated security staff to investigate every false positive alone.
4. Educate and Train the Entire Team
Workflow integration only goes so far if people do not understand what they are looking at. Basic security training for every employee — not just engineers — is a high-leverage investment. Key topics to cover include:
- Phishing and social engineering: How to recognize suspicious emails, links, and requests, and what to do when you spot them.
- Authentication hygiene: How to use multi-factor authentication (MFA), password managers, and single sign-on (SSO) tools correctly.
- Network safety: Which networks are safe to use, when to use a VPN, and how to stay secure while traveling for work.
- Physical security basics: Locking screens when stepping away, never plugging in unfamiliar USB devices, and following a clean-desk policy.
The goal is to raise the organization’s collective security IQ to a level that makes you an unappealing target. A well-trained team generates fewer incidents, which directly reduces the workload on your security staff.
5. Choose Comprehensive, Integrated Security Tools
Tool sprawl is a silent productivity killer for security teams. When alerts come from a dozen disconnected systems, analysts spend more time correlating data than actually responding to threats. Aim for a single-pane-of-glass approach: one platform — or a tightly integrated set of platforms — that gives your security team a unified view of your network, infrastructure, and application layer.
When evaluating security platforms, look for native integrations with the tools your teams already rely on, such as:
- Incident management tools (e.g., PagerDuty, VictorOps / Splunk On-Call)
- Chat and collaboration platforms (e.g., Slack, Microsoft Teams)
- Cloud provider consoles and APIs (e.g., AWS Security Hub, Azure Defender, GCP Security Command Center)
- CI/CD pipelines, so that security scanning happens automatically at build time
A unified toolset enables proactive vulnerability management: your team can identify and remediate weaknesses before they are exploited, rather than scrambling to contain a breach after the fact. Over time, it also builds an institutional knowledge base about your security posture and how your systems and users behave under normal conditions — making anomalies far easier to spot.
Putting It All Together
Security talent will continue to be expensive and difficult to hire for the foreseeable future. Rather than waiting for the market to change, forward-thinking organizations are restructuring how security work gets done — distributing ownership across development, operations, and the entire business, and equipping everyone with the tools and knowledge they need to contribute.
By embedding security into existing DevOps workflows, training your full team, and consolidating your tooling, you give your dedicated security professionals the leverage they need to operate strategically rather than reactively. The result is a more resilient organization and a security team that can actually scale with the business.
Originally sourced from business2community.com.