Originally reported by The Register (theregister.co.uk), May 2020. This article expands on the original source coverage for a DevOps engineering audience.
GitLab 13.0: The 2020 Major Release
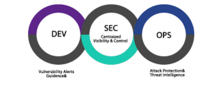
GitLab 13.0 landed in May 2020 as the company’s headline release for the year. While GitHub remains the dominant player in hosted code repositories — with Atlassian’s Bitbucket also widely used — GitLab occupies a distinct market position: a single, integrated platform for the entire DevSecOps lifecycle, from planning and source control through CI/CD, security scanning, Kubernetes management, and monitoring.
Unlike GitHub or Bitbucket, the core of GitLab is open source. The free Community Edition is a popular choice for self-hosted installations, giving organisations full control over their data and infrastructure.
Key New Features in GitLab 13.0
Gitaly Cluster: High-Availability Git at Scale
The headline infrastructure improvement in 13.0 is Gitaly Cluster support. Brendan O’Leary, GitLab’s senior developer evangelist at the time, explained the problem it solves:
“Git itself can be hard to scale — it is a filesystem-based database. That works great on NFS, but in the cloud world it’s a challenge. Our solution has been the open-source product Gitaly, which is a gRPC layer between Git and a system that’s consuming Git. What’s coming in 13.0 is Gitaly Clusters, which is the ability to have multiple write destinations, so you can now shard your data and have it be highly available. It removes the requirement for NFS.”
— Brendan O’Leary, Senior Developer Evangelist, GitLab
For engineering teams running large self-managed GitLab installations, this matters significantly. NFS-based Git storage has long been a reliability and performance bottleneck. Gitaly Cluster replaces that dependency with a replicated, highly available architecture suitable for cloud-native deployments.
Security Enhancements: CVE Authority, .NET SAST, and DAST for REST APIs
Security is a major theme in 13.0, reflecting GitLab’s positioning as a DevSecOps platform rather than simply a DevOps one:
- CVE Numbering Authority: GitLab became a CVE Numbering Authority (CNA), meaning teams can request CVE identifiers directly from within the GitLab UI. This simplifies responsible disclosure workflows for open-source projects hosted on GitLab.
- SAST for .NET Framework: Static Application Security Testing (SAST) coverage was extended to .NET Framework code. Previously, only .NET Core was supported.
- DAST for REST APIs: Dynamic Application Security Testing now supports REST APIs, covering a critical attack surface in modern microservices architectures.
Design Management Moves to Community Edition
A significant benefit for free-tier users: Design Management, previously restricted to GitLab Premium, is now available in the Community Edition. This feature allows designers and product contributors to upload and discuss design assets directly within GitLab issues, keeping design review in the same workflow as code review.
Progressive Delivery and Feature Flags
Progressive Delivery — releasing features to a subset of users before a full rollout — received further investment in 13.0:
- Feature flag lists now have full API support for create, edit, and delete operations, enabling automation in release pipelines.
- A/B testing based on feature flags was flagged as an upcoming capability.
- The ability to create feature flags directly from merge requests was also on the near-term roadmap at the time of release.
Does GitLab Play Nicely with the Rest of the DevOps Ecosystem?
GitLab’s all-in-one ambition is both its key differentiator and a source of friction with the broader DevOps tooling ecosystem. Specialist vendors — in security scanning, monitoring, artifact management, and other areas — view GitLab’s expanding feature set as competitive pressure.
O’Leary acknowledged the tension and described how GitLab is addressing it:
“We think that the more you can adopt a single application the more benefits you get, but that’s not realistic for an enterprise tomorrow — they’re not going to throw everything they have out. We have in our handbook that we need to interoperate with others, and we’ve got a lot better at that recently. We’ve got an ecosystem team now that’s responsible for how we play with others, and we didn’t used to have that. Another thing we’ve added is first-class support for other security scanning integrations.”
— Brendan O’Leary, Senior Developer Evangelist, GitLab
For DevOps engineers evaluating GitLab in organisations with established toolchains, this is a practical consideration. GitLab’s pipeline architecture supports third-party integrations through its CI/CD configuration, and the addition of an ecosystem team signals a shift from a purely “replace everything” posture toward genuine interoperability.
GitLab’s Development Model: Open and Iterative
GitLab operates as a fully remote company and applies Agile minimum viable product (MVP) principles to its own development. New features are introduced with core functionality and refined through subsequent releases. Because development progress is publicly visible, engineers can track upcoming features well before they ship — reducing surprise and enabling better adoption planning.
The company published both video and text “kickoff” content for the 13.0 release, consistent with its handbook-driven, transparent culture.
Context: Remote Work and the 2020 Market
GitLab 13.0 launched during the early months of the COVID-19 pandemic, a period when remote work went from optional to mandatory for most software teams globally. O’Leary noted a significant uptick in interest in remote work practices, an area where GitLab — as a fully distributed company — had years of documented experience and public handbook content to share.
Summary
| Feature Area | What’s New in 13.0 | Edition |
|---|---|---|
| Infrastructure | Gitaly Cluster (HA Git, no NFS required) | All |
| Security | CVE NCA status; SAST for .NET Framework; DAST for REST APIs | Ultimate / varies |
| Design | Design Management moved to Community Edition | Community (free) |
| Progressive Delivery | Feature flags API; A/B testing (roadmap) | Premium+ |
| Ecosystem | New ecosystem team; third-party security scanner support | All |
GitLab 13.0 represents a meaningful step in GitLab’s DevSecOps maturity, particularly for teams running large self-managed deployments who will benefit from Gitaly Cluster, and for Community Edition users gaining design tooling. The continued investment in security capabilities and ecosystem interoperability makes it a release worth evaluating even for organisations not fully committed to the GitLab-only stack.