This article is based on source material originally published on securityboulevard.com.
Introduction
DevOps combines software development and IT operations into a unified practice. It emerged from the need to bridge the communication gap between developers and operations teams, enabling faster delivery cycles and more reliable deployments. By treating operational concerns as first-class parts of the development process, DevOps allows teams to automate deployments, increase visibility, and ship software with minimal friction.
However, as security requirements become more demanding and attack surfaces expand—particularly with the growth of cloud-native architectures—many organizations are finding that DevOps alone is not enough. The natural evolution of this approach is DevSecOps: a model that integrates security practices directly into the DevOps pipeline rather than treating them as an afterthought.
This article explains what DevSecOps is, how it differs from DevOps, where to begin as a practitioner, and why making the shift delivers measurable security benefits.
What Is DevSecOps?
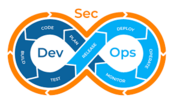
DevSecOps extends the DevOps philosophy by making security a shared responsibility across the entire software delivery lifecycle. Rather than adding security controls at the end of a release cycle—or delegating them entirely to a dedicated security operations centre (SOC)—DevSecOps embeds security thinking into every phase: planning, coding, testing, deployment, and monitoring.
In traditional development models, three teams operated in sequence:
- Development: Builds the application.
- Operations: Deploys and maintains it.
- Security: Attempts to harden it after the fact.
DevSecOps replaces this sequential, siloed model with a collaborative one in which all three disciplines contribute simultaneously. Security is designed into the application from the outset, not bolted on at the end. This results in fewer vulnerabilities reaching production, faster remediation of those that are found, and a more defensible audit trail.
How DevSecOps Differs from DevOps
The core difference is when security enters the process. In many DevOps workflows, security reviews happen late in the pipeline—often just before a release. This creates bottlenecks and, more critically, means that security issues are discovered at the most expensive point to fix them.
DevSecOps applies the principle of shift-left security: moving security checks and controls earlier in the development lifecycle. Practical examples include:
- Threat modelling during design: Identifying potential attack vectors before a single line of code is written.
- Static application security testing (SAST): Scanning code for vulnerabilities as part of every pull request or commit.
- Software composition analysis (SCA): Checking third-party libraries and dependencies for known vulnerabilities.
- Container image scanning: Verifying that base images and runtime environments meet security standards before deployment.
- Dynamic application security testing (DAST): Running automated penetration tests against running services in staging environments.
- Infrastructure-as-code (IaC) scanning: Detecting insecure configurations in Terraform, CloudFormation, or Kubernetes manifests before they are applied.
Each of these practices can be automated and integrated into a CI/CD pipeline, preserving the speed that DevOps is known for while adding meaningful security gates.
Where Does a DevSecOps Practitioner Get Started?
DevSecOps roles draw from a wide range of backgrounds—software engineers, network engineers, systems architects, and information security analysts. There is no single prescribed career path, but there are a few foundational areas that every DevSecOps practitioner should understand:
1. Understand the Existing DevOps Pipeline
Before embedding security into a pipeline, you need a thorough understanding of how that pipeline works. Know your CI/CD tooling (Jenkins, GitHub Actions, GitLab CI, etc.), your container orchestration platform, your artifact repositories, and your deployment targets. Security controls can only be integrated where you have visibility and access.
2. Build a Working Knowledge of Information Security
You do not need to be a certified penetration tester, but you do need to understand core security concepts: the OWASP Top 10, common cryptographic patterns, authentication and authorisation mechanisms, network security fundamentals, and secure coding practices for the languages your team uses. Without this grounding, you cannot make credible recommendations to developers.
3. Learn Cloud Security Fundamentals
Most modern applications run on cloud infrastructure. IAM policies, storage bucket permissions, network security groups, secrets management, and logging configurations are all areas where misconfigurations are common and consequential. Understanding how your cloud provider’s shared responsibility model works is essential.
4. Champion Organisational Buy-In
DevSecOps cannot succeed as a grassroots effort alone. Leadership must commit to it. This means accepting that some security gates will occasionally slow a release, funding the tooling and training required, and shifting the cultural expectation so that security is everyone’s responsibility—not just the SOC’s.
Why DevSecOps? The Core Benefits
Automated Security Auditing
Just as DevOps automates build and deployment tasks, DevSecOps automates security testing. Automated scanners run against every code commit, container build, and infrastructure change. This means security checks happen continuously rather than periodically, dramatically reducing the window between vulnerability introduction and detection.
Earlier and Cheaper Defect Detection
Security defects found during development are significantly cheaper to fix than those found in production. A failed security test in a CI pipeline is a feature, not a problem: it means the system caught an issue before it reached a customer.
Comprehensive Audit Trails
DevSecOps mandates detailed logging at every stage of the pipeline. Every commit, build, test result, deployment, and configuration change is recorded. This audit trail is invaluable for compliance reporting, post-incident analysis, and demonstrating due diligence to auditors or regulators.
Reduced Blast Radius of Security Incidents
By catching vulnerabilities early and enforcing secure configurations throughout the pipeline, DevSecOps limits the opportunities for attackers to exploit weaknesses. Applications that are built with security in mind from the start present a smaller and better-defended attack surface.
The Cultural Shift: Breaking Down Silos
The technical changes required for DevSecOps are substantial, but the cultural changes are equally important and often harder to achieve. Historically, development, operations, and security teams have had competing priorities:
- Developers want to ship features quickly.
- Operations teams want stability.
- Security teams want controls that developers may see as obstacles.
DevSecOps reframes these competing interests as a shared goal: delivering secure, reliable software rapidly. This requires open communication, shared tooling, joint postmortems, and a blameless culture where a failing security test is treated as a learning opportunity rather than a reason to assign fault.
Practical steps to drive this cultural change include:
- Running cross-functional security training so that developers understand common vulnerability classes.
- Including security engineers in sprint planning and code reviews, not just at release gates.
- Defining shared security metrics (e.g., mean time to remediate a vulnerability) that all teams are accountable for.
- Celebrating security wins—when a test catches a critical bug before production, make that visible.
Conclusion
Transitioning from DevOps to DevSecOps is not simply a matter of adding new tools to an existing pipeline. It requires a deliberate shift in culture, process, and shared responsibility. Security must move from being a late-stage gate to an integrated discipline that informs every commit, every configuration change, and every deployment decision.
The organisations that make this transition successfully do so because leadership commits to it, teams are trained and empowered, and failure is treated as signal rather than blame. When security is everyone’s job, applications ship faster and more securely—and that is the fundamental promise of DevSecOps.
Start by auditing your current pipeline for natural security integration points, invest in the foundational security knowledge your team needs, and build incrementally. The shift is achievable, and the security posture improvements compound over time.